

CVSS 9.8 · HotNews · SAP Security Note 3759472 · No workaround
Heads-up: this is a technical deep-dive. We get into kernel opcode numbers, wire-format bytes, and MITRE ATT&CK mappings. If you’re an SAP Basis admin, a SOC analyst, or a security architect, this is written for you. If you just need the executive summary, jump to “What SAP customers should do this week.”
The 90-second version
On September 8, 2026, SAP shipped a HotNews-rated patch for CVE-2026-58240 — a missing authentication check in the SAP NetWeaver Message Server that lets any unauthenticated attacker with network access to the internal Message Server port register a rogue “ASCS gateway” component.
Once registered, the Message Server broadcasts the attacker’s forged trust entry to every subscribed application server in the landscape, polluting the trust list that underpins internal cross-instance authentication.
Four days later, a public write-up appeared on redrays.io with kernel binary analysis. Later that same day, a working proof-of-concept — check, register, verify, cleanup — was built by the SecurityBridge Research Lab.
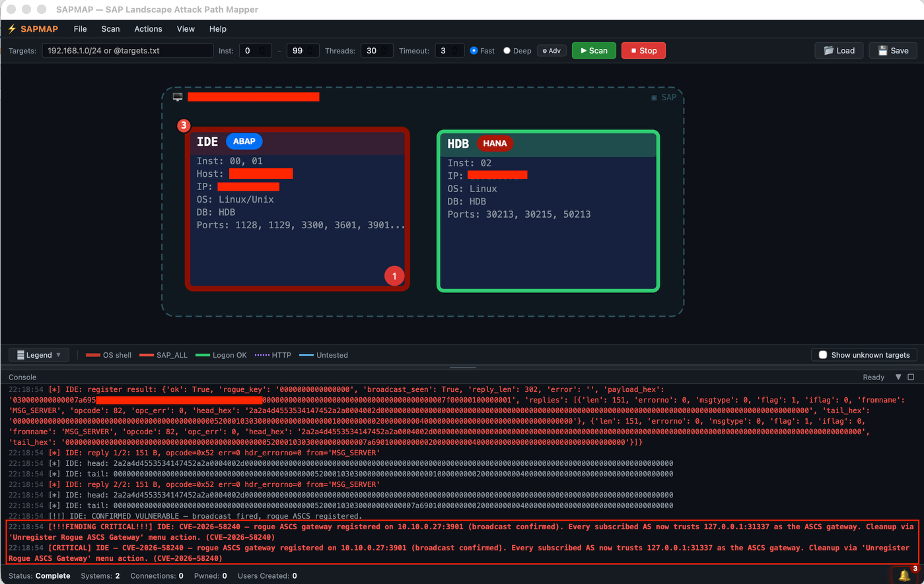 Working Proof-of-Concept for exploitation of CVE-2026-58240
Ninety-six hours from SAP Patch Day to end-to-end confirmed exploitation. That number would have been shorter if the lead researcher hadn’t been on holiday for the first two days.
What CVE-2026-58240 actually does
The SAP Message Server (MS) is the central directory for an SAP landscape. When an application server dispatcher starts up, it registers with the MS. When an AS wants to route an internal RFC call, coordinate an enqueue lock, or forward a trusted SSO2 ticket, it asks the MS where the central services live. Every subscribed AS trusts the MS’s answer.
CVE-2026-58240 is a missing authentication check on the MS opcode that writes the ASCS gateway entry. Any anonymous client that can complete the standardMS_LOGIN_2
handshake can send opcode0x52
(MS_ASCS_GW_LOGON) with a forged host, port, IP, and PID.
The kernel’sMsAscsGwReadPayload
parses the blob straight into the process-globalgAscsGw
struct, sets_ZL12gAscsGwValid = 1,
and callsMsSSndAscsGwInfo — which broadcasts the new gateway identity to every AS that subscribed to gateway updates.
There is no ACL check on the write itself. The MS’sms/acl_info
list — the standard defence against Message Server abuse — is IP-based and doesn’t gate this opcode family. The kernel patch adds a post-parse check that the LOGON must arrive on the internal port AND from the ASCS host: five new trace strings mark the fixed code path (“ASCS gateway is already logged on”, “not made on the internal port”, “not made from the ASCS host”, “ASCS gateway logon from”, “ASCS gateway logoff”).
What this gives an attacker
- Trust-list pollution. Every AS in the landscape now believes the ASCS gateway is at
<attacker_ip>:<attacker_port>.
Trust decisions that route through the ASCS — SSO2 ticket relay, enqueue coordination, internal RFC callbacks — now traverse an attacker-controlled endpoint. - Adversary-in-the-middle. With a listener on the forged endpoint, the attacker intercepts internal traffic that would normally never leave the SAP landscape’s trusted perimeter.
- Pre-auth impact. No SAP credentials required. No SSO ticket needed. No local access. A single unauthenticated TCP connection to the internal MS port is enough.
SAP scored it 9.8 with Pre-auth RCE, Remote Code Execution, and Trust-list Pollution in the “Other Terms” field. That framing is deliberate. Trust-list pollution IS the primitive — everything else falls out of chaining it with whatever the attacker wants to do next.
Why the compensating controls aren’t enough
Two configurations meaningfully reduce exposure:
ms/acl_info— populated correctly, restricts which hosts can even completeMS_LOGIN_2.
It does NOT close the vulnerability by itself — if the attacker gains a foothold on any host in the ACL list (typically every application server in the landscape), the exploit becomes reachable via that pivot.system/secure_communication = ON
(orms/enforce_secure_communication = ON) — the MS internal port only accepts TLS connections with a SAP SystemPKI client certificate. This IS a robust wire-layer block: without a landscape-signed cert, no attacker can even reach the vulnerable opcode. But it’s defence in depth, not a replacement for the patch — if the parameter is ever toggled off, the exposure surface opens the same day.
The only durable fix is the kernel patch. SAP Security Note 3759472 delivers it as a binary patch — no workaround, no profile parameter to flip, nothing to do except run the kernel update.
Fixed kernel levels
| Kernel line | Fix level |
|---|---|
| 9.16 | PL100 |
| 9.18 | PL032 |
| 9.19 | PL017 |
| 9.20 | PL007 |
Older kernels (7.x, 8.x) don’t ship the ASCS_GW opcode family and are not affected by this note. If your S/4HANA landscape is on the 9.x kernel line — which is now the mainstream S/4 codeline — you’re in scope.
The compressed timeline: 96 hours, not 96 days
Historically, SAP customers have had months between an SAP note and public exploit tooling. That gap is closing fast.
Timeline for CVE-2026-58240 (SecurityBridge Research Lab)
- Sep 8, 2026 — SAP publishes Note 3759472 as HotNews.
- Sep 9–10, 2026 — Our lead researcher is on holiday. The CVE waits.
- Sep 11, 2026 — SecurityBridge Research Lab begins work: kernel diff, opcode analysis, defensive-tooling detection code drafted.
- Sep 12, 2026 (morning) — redrays.io publishes a technical analysis with kernel binary diff, five new trace strings identified, opcode numbers reversed, partial screenshot of the wire format.
- Sep 12, 2026 (afternoon) — SecurityBridge Research Lab ships the detection code (opcode presence check on the anonymous
MS_LOGIN_2path). - Sep 12, 2026 (evening) — Wire format fully reverse-engineered against an unpatched lab system. First confirmed end-to-end exploit fires: rogue port
0x7a69
appears in theMsSSndAscsGwInfo
broadcast body at bytes 7-8, exactly as the assembly analysis predicted. Verified cleanup path also lands.
That compression has structural causes worth naming:
- Modern reverse-engineering tools. Kernel binary diffing between patched and unpatched builds surfaces the vulnerable opcode within hours.
- Public research culture. Kernel-level SAP research is no longer siloed; write-ups appear on public blogs the week of the patch.
- AI-accelerated development. This is the newer variable, and it deserves an honest section of its own.
The AI angle: what changed, and what didn’t
The proof-of-concept for CVE-2026-58240 that lands in defensive tooling within 96 hours of the SAP note was built collaboratively with an AI coding assistant. That’s not marketing hype — it’s a factual change in the development-time economics of security tooling.
What AI actually accelerated
- Wire-format reverse-engineering. Once we had a partial payload fragment from a public screenshot, iterating on payload byte layouts against a live unpatched target — try shape A, observe response, try shape B, compare, converge — is exactly the kind of tight-loop work AI assistants excel at. The winning 57-byte layout
(03 | 00×6 | port_be | host_40 | ip_4 | pid_be_4)
was pinned down inside an hour of guided fuzzing. - Wide-surface integration. A well-designed PoC touches a dozen files: the wire protocol module, the scanner integration, the GUI menu, the finding schema, the ATT&CK map, the engagement report, the remediation database, the test suite. Wiring those consistently used to be days of careful editing. Now it’s a coordinated multi-file change with the same care, done in an afternoon.
- Test authoring. Byte-fixture regression tests capturing the exact wire capture of the confirmed exploit — the kind of test that prevents future refactors from silently breaking the detector — no longer feels like a chore.
What AI didn’t change
- Understanding the mechanism. Someone still had to read the SAP note, understand
gAscsGw,
understandMsSSndAscsGwInfo,
and understand why the port-echo is the definitive success signal instead of the hostname. AI accelerates execution; it doesn’t replace judgement. - Access to a target. The wire-format reversal needed a live unpatched box to fuzz against. That constraint hasn’t moved.
- The compensating-control nuance. Distinguishing a
system/secure_communication
block (TLS-only listener) from anms/acl_info
rejection (errno 236) required understanding both mechanisms and building the TLS-probe detector. AI helped write the code; it took a human researcher to know we needed it.
What SAP customers should do this week
Immediate actions
- Identify every 9.x kernel instance below fix level. SecurityBridge Platform inventories kernel PLs across the landscape — filter for anything on 9.16 <PL100, 9.18 <PL032, 9.19 <PL017, or 9.20 <PL007.
- Apply SAP Note 3759472. Kernel binary patch, ASCS instance restart. No workaround exists.
- Verify the patch landed. The SecurityBridge Platform can help you there.
Defence in depth
- Turn on
system/secure_communication
if it isn’t already. This blocks the wire-level exploit path regardless of patch status and is a robust setting to leave enabled permanently. - Tighten
ms/acl_info.
Application-server hosts only, no wildcards. This limits blast radius even when secure communication is temporarily disabled. - Firewall the internal MS port (39NN) to the SAP application-server subnet. The internal MS should never be reachable from a general workstation VLAN.
How SecurityBridge Platform helps
Security & Compliance module — continuously scans your landscape for exactly the parameters that decide your exposure to CVE-2026-58240 and its family:ms/acl_info,system/secure_communication,snc/enable,
etc., and the accompanying kernel patch levels. If a parameter drifts — during a system copy, a support-package application, or a troubleshooting session — the platform flags it before an attacker notices.
Threat Detection module — SecurityBridge Platform closes that gap: we actively monitor for post-exploitation behaviours — anomalous cross-instance RFC routing, unexpected ticket-relay paths, and specific SAL / SysLog patterns.
Closing thought
The right lesson from CVE-2026-58240 is not “AI made SAP security harder.” What’s changing is the timeline symmetry: attackers and defenders now converge on public knowledge of a CVE at roughly the same rate.
That symmetry only pays off for defenders who patch fast. The customers who apply SAP Note 3759472 this week will read this article and nod. The customers who don’t will read a very different article in a few months, and it won’t be from SecurityBridge — it’ll be from a breach-notification lawyer.
Don’t be that second customer.
SecurityBridge Platform’s Security & Compliance module identifies every affected system against Note 3759472 within minutes — including which of your instances havesystem/secure_communication
disabled and how tight yourms/acl_info
really is. Contact your account team for a walkthrough.